Scala Communications i-ask admin site hit by unauthorized access
Five well-known Japanese companies were caught up at once because they all stored customer inquiries with the same vendor. Scala Communications sells i-ask, a system companies use to publish FAQ pages and to receive and track the questions customers send through their websites. Daiwa Securities and the other firms run their inquiry handling on it, which makes Scala their contractor.
The inquiries of up to five client firms sat on one Scala server, and that server is where the intruder got in. Scala puts the total at up to 713,126 records.
Each inquiry counts once, so someone who wrote in several times is counted several times. Scala is still matching duplicates to find out how many people that is.
Scala Communications is a subsidiary of Scala, Inc., listed on the Standard market of the Tokyo Stock Exchange (code 4845). In the same week Daiichikosho, the operator of the Big Echo karaoke chain, reported a separate leak at a different contractor. That case is covered in Big Echo data breach: 8.72M records may be exposed.
Data leak window: unauthorized access from October 2 to October 3
The intruder was inside overnight, from about 20:30 on Friday, October 2 until about 08:00 the next morning. Using the i-ask admin login, the intruder installed a malicious program on Scala's server. From there, Scala says, inquiry data in the client databases on the same server may have been copied out.
A database monitoring alert went off on the morning of October 3. Scala started looking into it, shut the intruder out at about 08:00 and told the affected clients that day. The disclosures followed over the next five days.
From the break-in to the last disclosure (from Scala's and the clients' notices)
| Date and time (JST) | What happened |
|---|---|
| Oct 2, about 20:30 | Intruder logs into the i-ask admin site and plants a malicious program |
| Oct 3, morning | A database monitoring alert prompts Scala to investigate |
| Oct 3, about 08:00 | Scala cuts off the access and tells affected clients the same day |
| Oct 5 | Daiwa Securities discloses |
| Oct 6 | Scala Communications and Citizen Watch disclose |
| Oct 7 | Sompo Japan and Tobu Railway disclose |
| Oct 8 | ORIX Life Insurance discloses |
Four of the clients, Daiwa, Citizen, Sompo Japan and Tobu, give tighter times relayed from Scala: 20:33 on October 2 to 08:01 on October 3. Scala's own notice rounds them to the half hour.
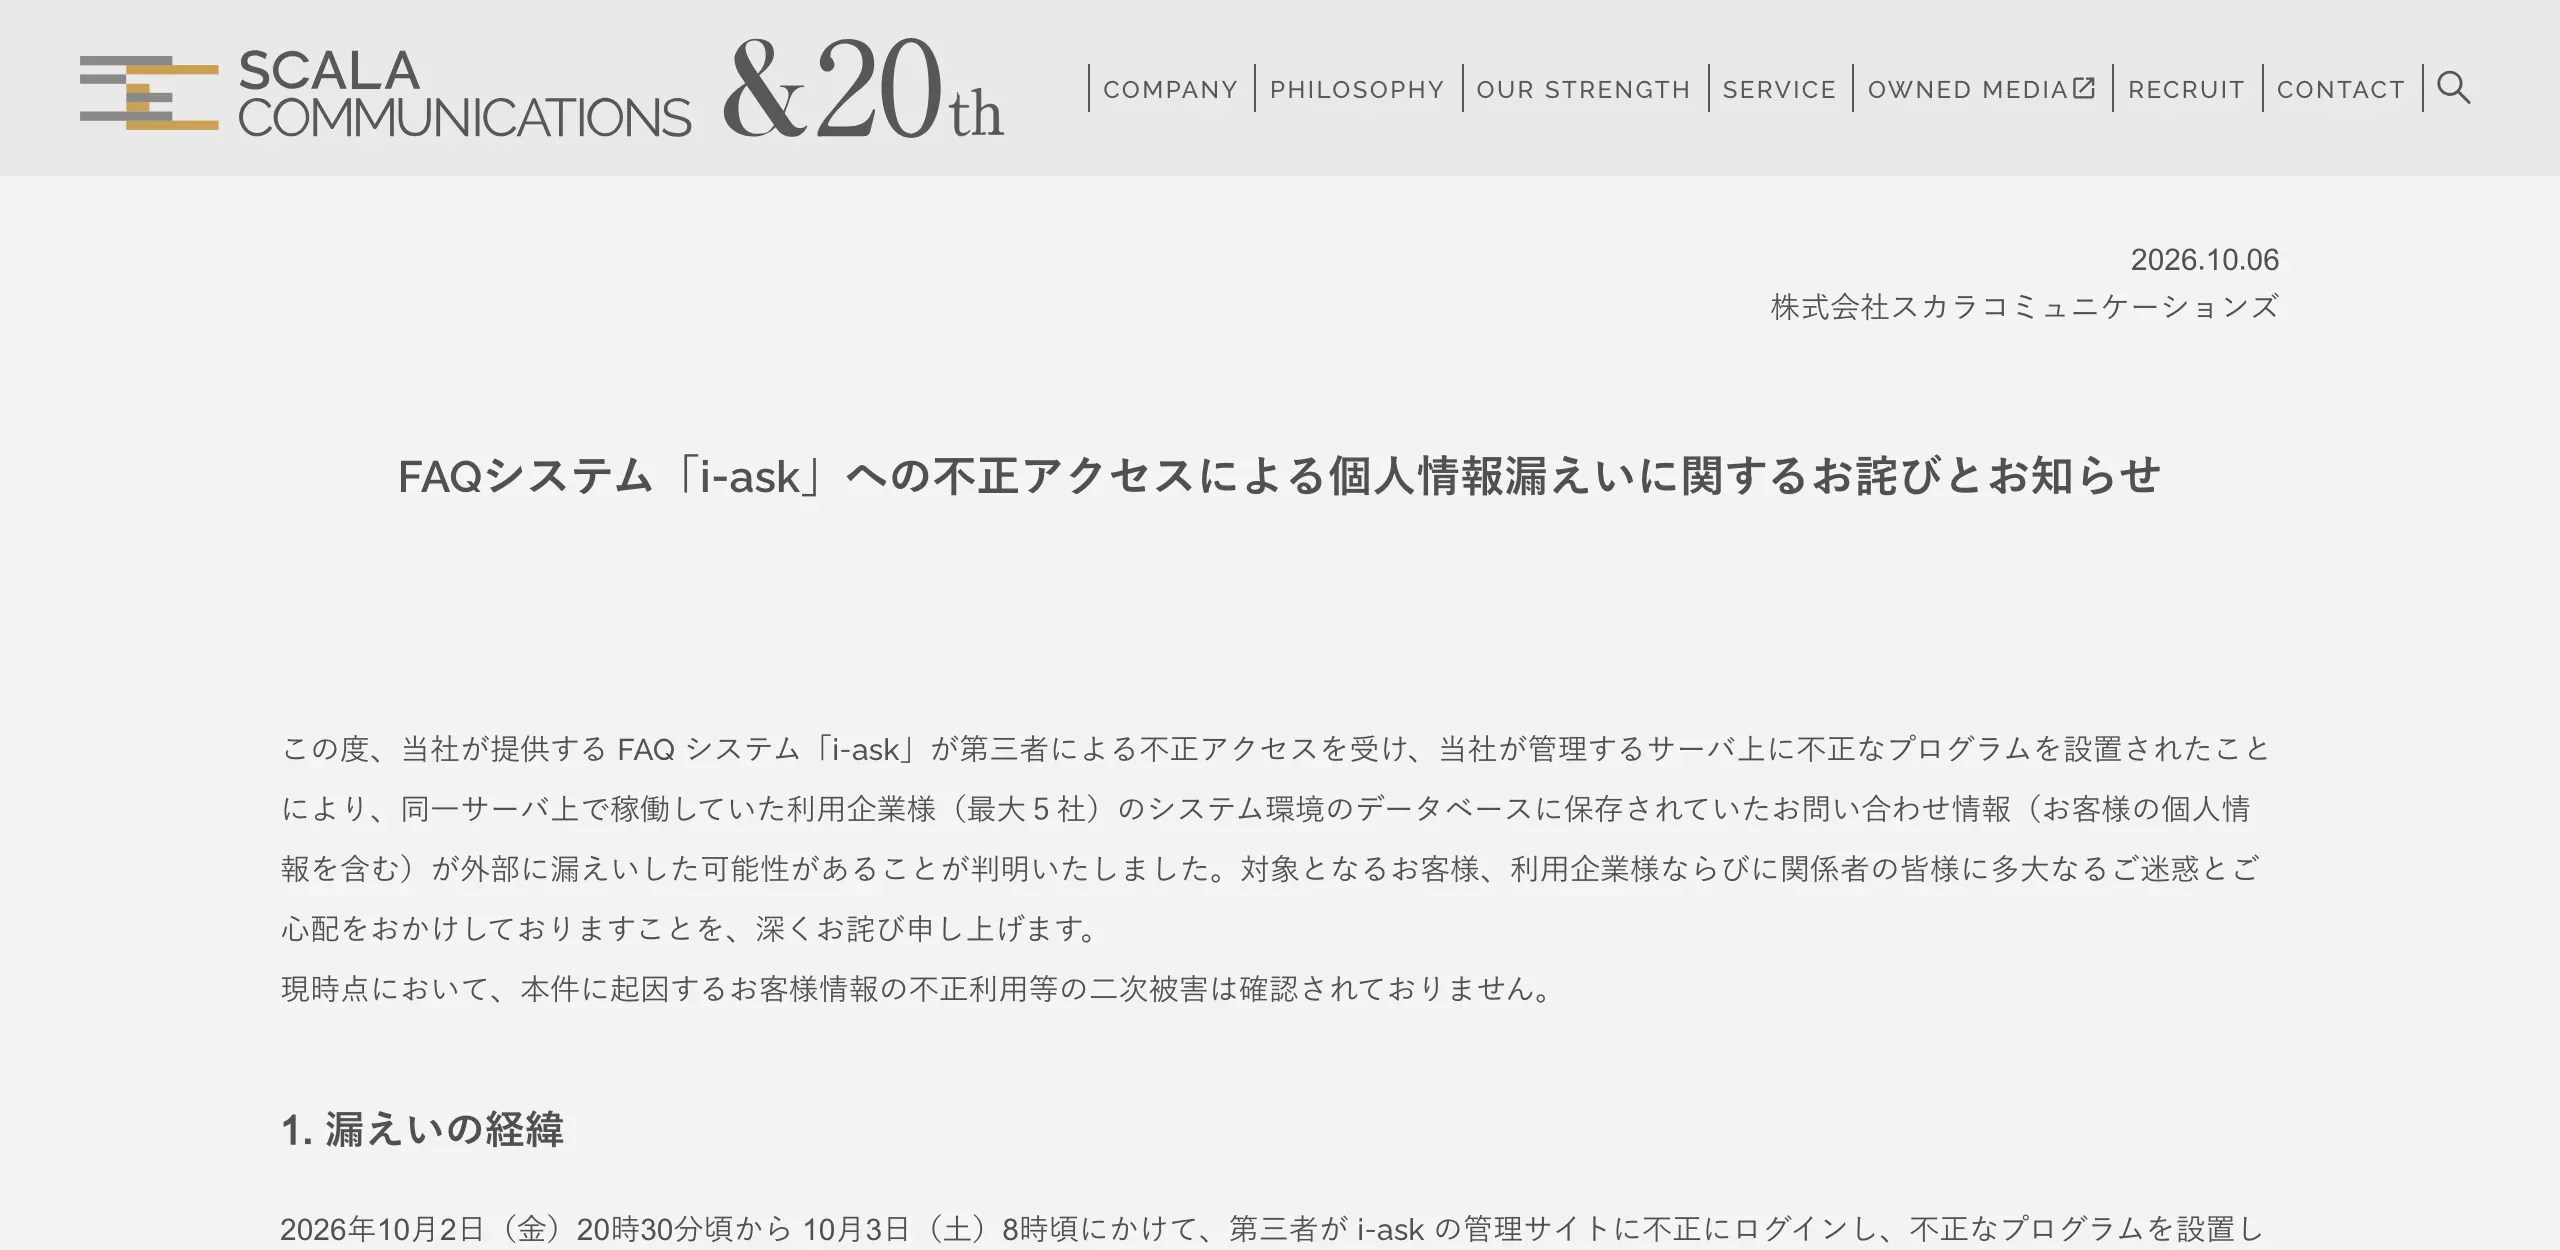
"2026年10月2日(金)20時30分頃から 10月3日(土)8時頃にかけて、第三者が i-ask の管理サイトに不正にログインし、不正なプログラムを設置したうえで、同一サーバ上の利用企業様のシステム環境のデータベースからお問い合わせ情報を取得された可能性があることを確認しております。" — from section 1, how the leak happenedView official source →
Personal information and data leak details from five client firms
Scala did not name its clients, but five firms have come forward on their own. Each one published the scale and type of data it believes was exposed. "What each client firm disclosed" lists them in the order they came forward.
What each client firm disclosed (from each firm's notice)
| Firm | Disclosed | Scale |
|---|---|---|
| Daiwa Securities | Oct 5 | About 110,000 customers (about 220,000 records in all) |
| Citizen Watch | Oct 6 | About 100,000 people |
| Sompo Japan | Oct 7 | About 60,000 inquiry records |
| Tobu Railway | Oct 7 | No count given (no sign its data was viewed or taken) |
| ORIX Life Insurance | Oct 8 | About 26,500 inquiry records |
The figures are not like for like. Daiwa and Citizen count people, while Sompo Japan and ORIX Life count inquiries with repeats included. Adding them up would mix the two, so the only overall total is Scala's 713,126.
Daiwa: account number and email address of 110,000 clients
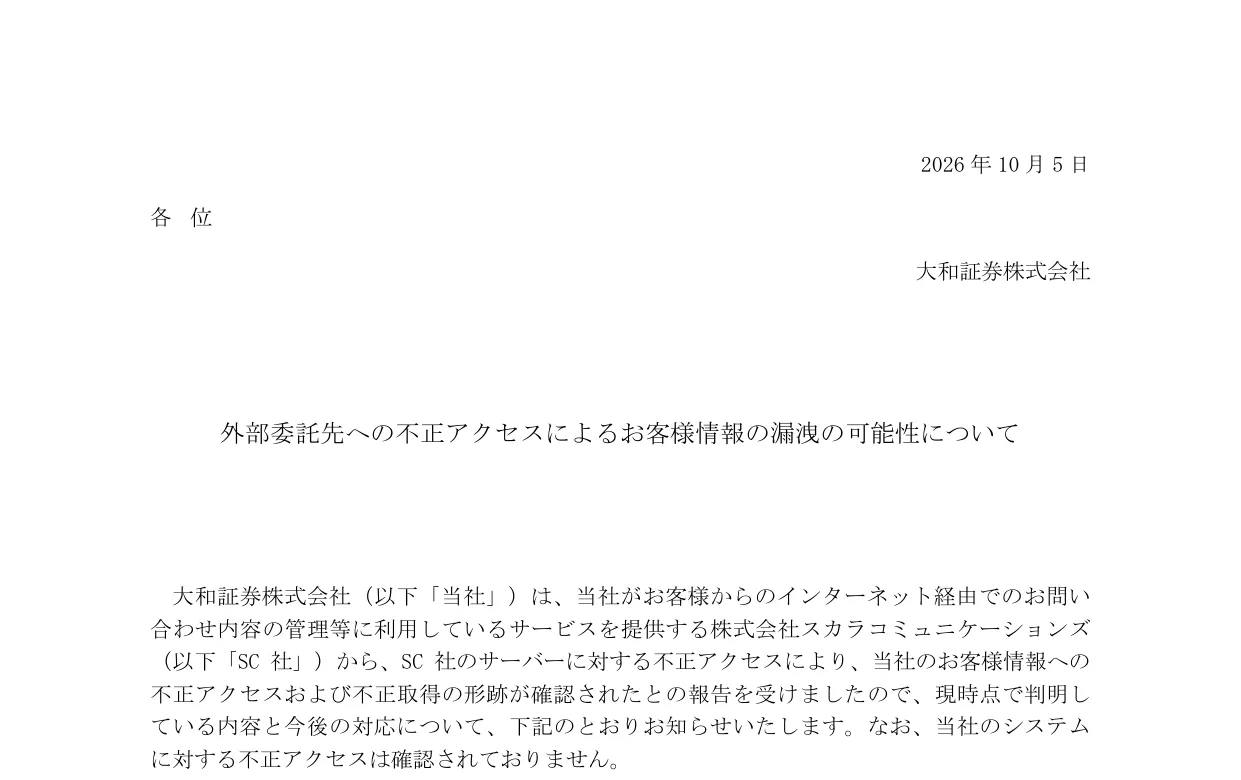
Daiwa Securities says names, email addresses, account numbers and other details of about 110,000 customers may have leaked. Counting inquiries that carry no identifying details, the total is about 220,000 records. Daiwa used i-ask to manage questions sent in online, and its inquiry history was stored on Scala's server.
Daiwa says the exposed data, account numbers included, cannot be used to log in or to trade, including through its online trading service. It has found no improper trades and no sign the data has been posted online.
Citizen Watch: names, phone numbers and addresses of 100,000 people
Citizen Watch says names, addresses, phone numbers and email addresses of about 100,000 people are involved. The data came from the contact forms on its Citizen, Bulova and Frederique Constant websites. Anyone who typed bank or card details into the message box should assume those were exposed as well.
Citizen's online store, the MY CITIZEN membership service and its internal systems were not touched. The company had already stopped taking new inquiries through the system, and it plans to shut it down in mid-October 2026 and delete the personal data stored there.
Sompo Japan: 60,000 inquiries about its dashcam service
Sompo Japan says about 60,000 inquiry records tied to SMILING ROAD, its connected dashcam service for businesses, may have leaked. Most of the questions came from employees of companies that use the service, and repeat inquiries are counted each time. The exposed fields go beyond contact details:
- Names, phone numbers, addresses and email addresses
- Employer details such as company and department name
- Driver IDs and the type and time of driving alerts
- Dashcam serial numbers and application numbers
- The subject and body of each inquiry
A driver ID is the number a business gives each of its drivers to review their driving and coach them. Bank account, credit card and My Number card data were not included.
ORIX Life Insurance: medical personal information in 26,500 records
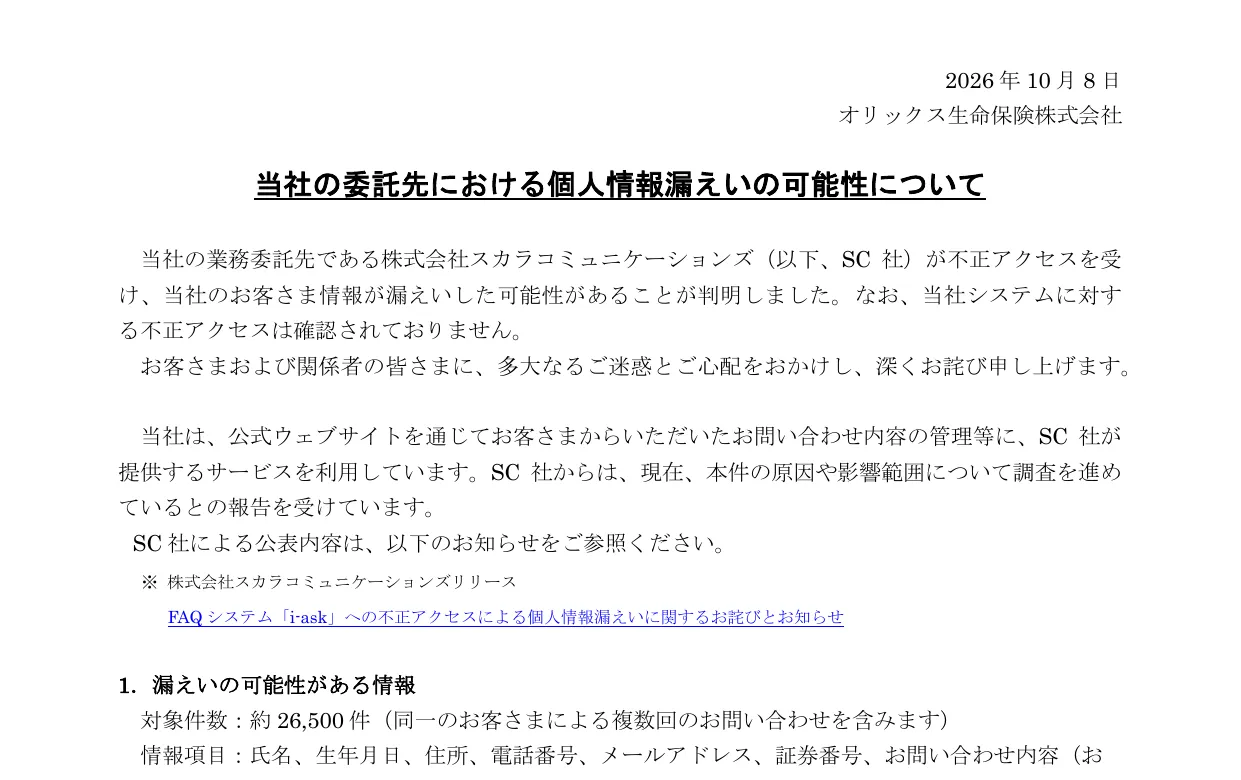
ORIX Life Insurance says about 26,500 inquiry records may have leaked, and some include medical details customers shared. The count includes people who wrote in more than once. ORIX Life used i-ask to manage questions sent through its website.
The records hold names, dates of birth, addresses, phone numbers, email addresses, policy numbers and the inquiry text. My Number and credit card numbers were not included. ORIX Life will contact the people involved by letter or email.
Tobu Railway: no sign of data viewed after the unauthorized access
Tobu Railway used i-ask for its customer center contact form, but so far it has found no sign that any of its data was viewed or taken. It disclosed the incident on October 7, after Scala reported the break-in. Links and attachments in a suspicious email are how fake sign-in pages and malware reach you, so leaving them unopened is the safe choice.
"なお、漏洩した可能性のある本件情報では、オンライントレードも含め、お客様の証券口座へのアクセスや当社での各種取引はできません。" — from section 3, individual contact and points to noteView official source →
"情報項目:氏名、生年月日、住所、電話番号、メールアドレス、証券番号、お問い合わせ内容(お客さまから申告いただいた医療情報等を含みます)" — from section 1, information that may have leakedView official source →
Unauthorized access to personal information: cause still unknown
Scala has not said how the intruder got hold of a working admin login. It is running a forensic investigation with an outside specialist, which means going through server logs and other traces to work out how the intruder got in and what was taken. Scala has already taken four steps:
- Changed the password of the account used in the break-in, and the admin passwords in every environment
- Blocked the attacker's IP addresses
- Quarantined the malicious program
- Changed settings so uploaded files can no longer run as programs
Longer-term fixes will follow from the investigation. Scala has committed to the four measures below:
- Stronger admin logins, including multi-factor authentication
- Separation between environments
- Closer monitoring
- Regular vulnerability assessments by an outside firm
Multi-factor authentication asks for a second proof of identity, such as a code sent to a phone, on top of the password. Scala has reported the incident to Japan's Personal Information Protection Commission and has consulted the police.
No misuse of personal information or data leak online confirmed
None of the five firms found any intrusion into their own systems. The break-in was on Scala's server only. Scala and the four firms that reported exposed data say no misuse had been found when they disclosed.
Daiwa Securities, Sompo Japan and ORIX Life Insurance say they will review how they oversee contractors. Citizen Watch says it will tighten control of vendors that handle personal data, and Daiwa is also checking its other contractors.
"調査結果に基づき、管理者認証の強化(多要素認証の導入等)、環境間の分離、監視体制の強化、第三者による定期的な脆弱性診断の実施等の対策を講じてまいります。" — from section 3, current responseView official source →
Phishing email warnings after the Daiwa Securities data breach
If you have ever contacted one of these five firms, be wary of emails, texts and calls that claim to come from them or from Scala. Phishing means posing as a real company to get you to click a fake link or hand over passwords. Because the leaked records include what people actually asked about, a scam message could quote your own question back to you and look genuine.
Daiwa and Sompo Japan both warn of phone and email fraud that uses customers' names and inquiry details. The firms ask customers to do four things:
- Do not open links or attachments in suspicious emails or texts
- Never give out trading IDs, passwords, PINs or one-time passwords (Daiwa)
- Check any unexpected contact through a desk listed on the firm's official website
- Contact the local police if you suspect fraud (ORIX Life)
You do not need to call in to check. Daiwa, Citizen, Sompo Japan and ORIX Life will contact affected people one by one, and ORIX Life will write by letter or email.
Phone number and email address for each company's hotline
Each firm runs its own desk for this incident. The 0120 numbers are toll-free lines that work only from within Japan. From abroad, Citizen's web form and Scala's email address are the practical options.
Hotlines for the five clients and Scala (from each firm's notice)
| Firm | Contact | Hours (JST) |
|---|---|---|
| Daiwa Securities | 0120-851850 | 9:00 to 17:00, closed weekends and holidays |
| Citizen Watch | Dedicated web form | Online |
| Sompo Japan | 0120-268-567 | Weekdays 9:00 to 17:00 |
| Tobu Railway | 0120-983-861 | 9:00 to 18:00, weekends and holidays included |
| ORIX Life Insurance | 0120-330-053 | Monday to Friday 9:00 to 17:00 |
| Scala Communications | 03-6418-3973 / incident@scala-com.jp | Weekdays 9:00 to 17:00 |
Until the investigation ends, the safe habit is to reach these firms only through the numbers above or their official websites, never through a link in a message. Scala says it will publish any new findings as soon as they are confirmed.
"万が一、当社または利用企業様を装った不審なメールやお電話等が届いた場合は、記載されたURLや添付ファイルを開かず、パスワード等の重要な情報を提供されませんようご注意ください。" — from section 4, request to customersView official source →
FAQ
- Can someone trade from my Daiwa Securities account with the leaked data?
- No, according to Daiwa. The names, email addresses and account numbers that may have leaked are not enough to log in or trade, online trading included. Daiwa says it has seen no improper trades and will keep monitoring accounts.
- Does 713,126 mean 713,126 people were affected?
- No. Scala counts one record per inquiry, so a person who wrote in three times appears three times. The number of people is still being worked out, and Scala had not published it as of October 10.
- How will I know if my data was included?
- The firm you contacted will tell you. Daiwa Securities, Citizen Watch, Sompo Japan and ORIX Life Insurance all say they will reach affected people one by one, and ORIX Life will do so by letter or email. Tobu Railway has found no sign its data was touched.
Related articles
 Aflac data breach in Japan hits 4.4M customersThe Aflac data breach in Japan exposed data on about 4.4 million customers between June 10 and 25, 2026. What leaked, why it went unnoticed, and what to do.
 IDCF Cloud ransomware hits 495 Japanese clientsAn IDCF Cloud ransomware attack on Oct. 7, 2026, hit 495 companies and local governments in Japan. Data in four zones may only return from customer backups.
 AI cyber attack: AI agents hit 27 firms for $25In an AI cyber attack disclosed by Gambit Security, three open source AI agents breached at least 27 retailers and took 600,000+ cards for about $25 a target.
 AI hacking hit Korean banks: what is confirmedCrowdStrike says an attacker used the ARTEX AI hacking tool and LLMs on South Korean banks. What is confirmed, what regulators ordered, and what is unknown.