Nippon Columbia malware infection behind the Big Echo data breach
The Big Echo data breach did not start inside Daiichikosho. It started on a single PC at a contractor.
Daiichikosho runs Big Echo and several other karaoke and restaurant brands. It outsources some customer data work to Nippon Columbia Group (NCG), and an NCG employee's computer picked up malware, software built to break into a device and steal or damage data.
NCG found the infection, cut the PC off its network and checked what was on it before telling Daiichikosho. Daiichikosho went public three days after that report. The dates are below.
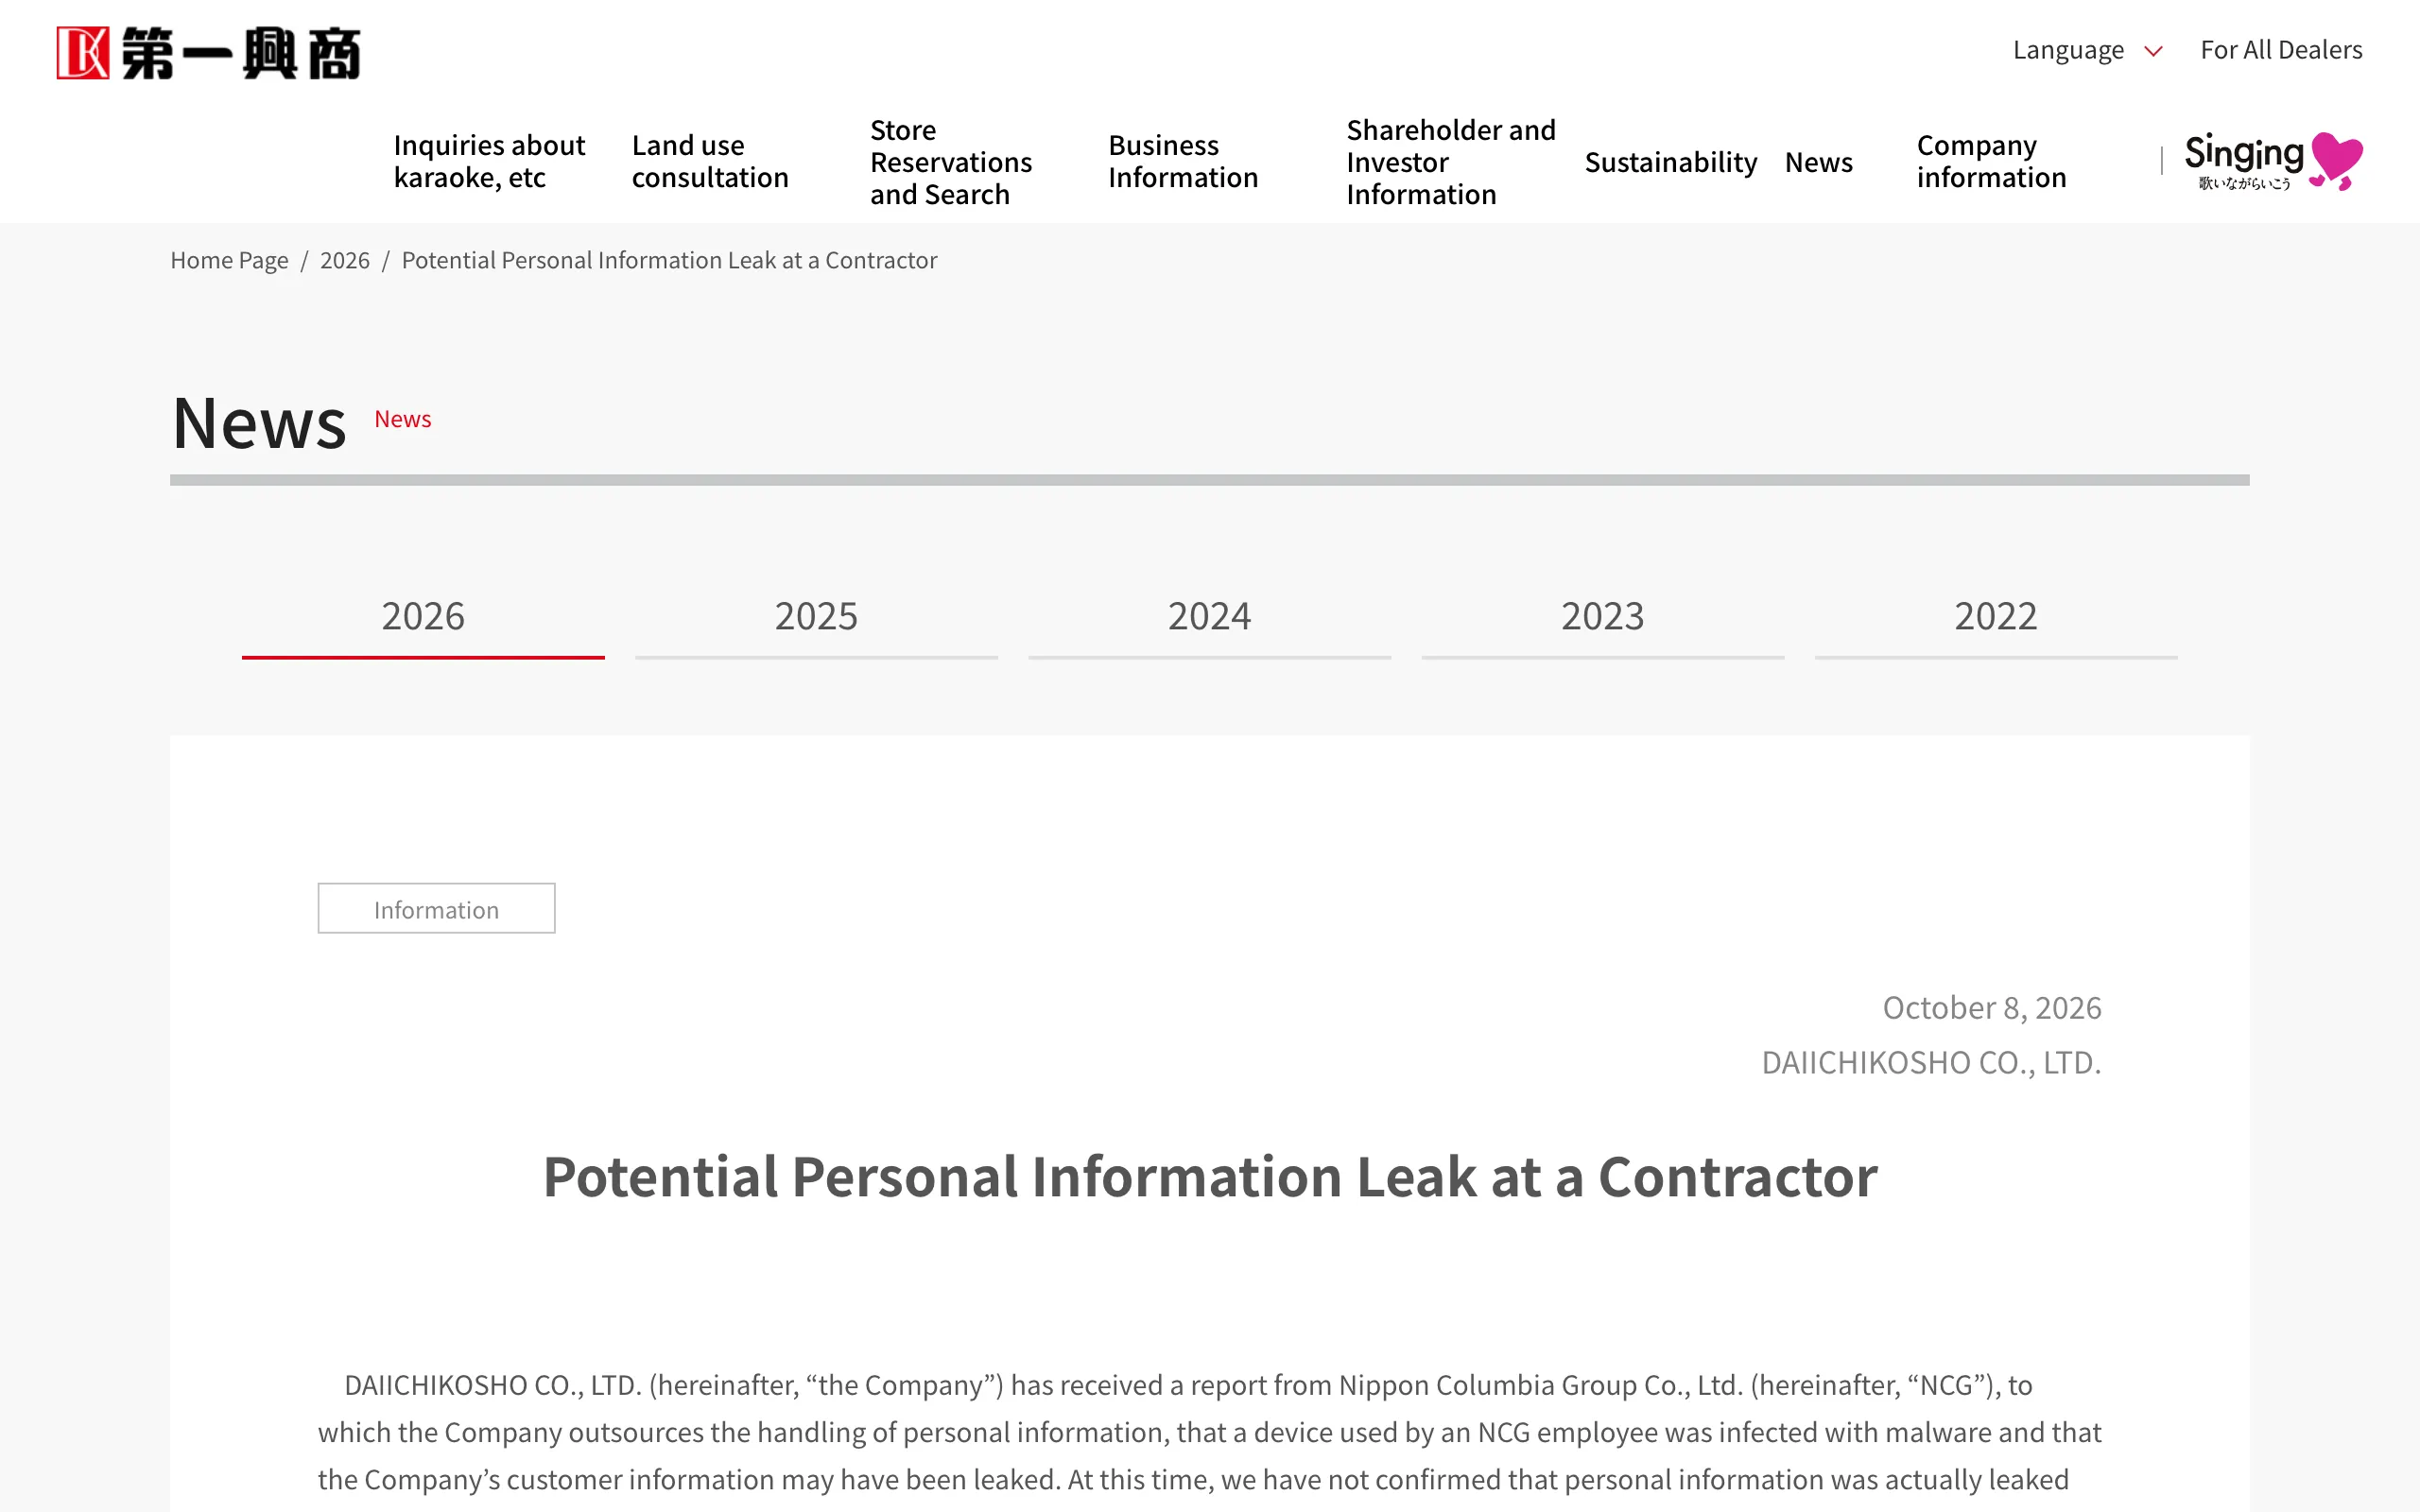
From infection to hotline (per Daiichikosho's notices)
| Date (2026) | What happened |
|---|---|
| October 1–2 | Malware found on one NCG employee PC |
| October 2 | NCG isolates the PC from its network |
| October 5 | NCG reports to Daiichikosho after checking the scope |
| October 8 | Daiichikosho announces a possible leak |
| October 9 | Daiichikosho opens a toll-free inquiry line |
Customer data from work Daiichikosho had outsourced was stored on that PC temporarily. Nobody yet knows whether it was copied off, and the company says it cannot rule that out. Monogatari Corporation disclosed a leak of 10,788,963 Yakiniku King app member records in the same week; we covered it in Yakiniku King data breach hits 10.79M app members.
"According to NCG, a device used by one of its employees (one PC) was found to be infected with malware between October 1 and October 2, 2026, and the device was isolated from the network on October 2. Following NCG’s investigation into the scope of the impact, the Company received a report from NCG on October 5." — "1. Incident Timeline and Report from NCG"View official source →
Personal data of 8.72 million karaoke customers and staff at risk
About 8,724,000 records may be exposed: 8,631,000 from customers and 93,000 from employees. The customer side covers people who signed up as members or booked at a Daiichikosho venue. Big Echo accounts for about 5.56 million of those records, roughly two in every three.
Records that may have leaked, by brand (per Daiichikosho)
| Brand or group | Records |
|---|---|
| BIG ECHO | about 5,558,000 |
| DK Dining | about 3,462,000 |
| Karaoke CLUB DAM | about 74,000 |
| MEGA BIG | about 43,000 |
| Banana Club | about 5,000 |
| B-GARAGE | about 4,000 |
| Duplicates removed | minus about 515,000 |
| Customer total | about 8,631,000 |
| Employees | about 93,000 |
| Total | about 8,724,000 |
The brand rows add up to more than the customer total because many people are on the books of more than one brand. Daiichikosho removed about 515,000 duplicates to reach 8,631,000.
Date of birth and phone number in the data leak, but no passwords
Five items are at risk: registered name, gender, date of birth, email address and phone number. The name is whatever the customer typed in when signing up, so it may not be a legal name.
Passwords are not in the data. Daiichikosho says the records alone cannot be used to spend a customer's points, and it has seen no unauthorized point use so far.
"Please note that passwords were not included in the information that may have been leaked, and this information alone cannot be used to redeem your points. To date, we have not confirmed any unauthorized use of points." — "3. Request to Our Customers"View official source →
Security breach cause still under investigation at Daiichikosho
Daiichikosho has not said what the malware was or how it got onto the PC. NCG has reset passwords and other login credentials and is still working out the cause and how far the damage goes, including whether anything left the device at all.
Daiichikosho says its own systems were not affected. As of October 9 it had found no misuse of personal data linked to the incident.
As a precaution, the company is checking its own systems. It will also go over the findings of NCG and outside specialists and reexamine how it manages contractors.
"We will review the investigation into the cause and the measures to prevent recurrence conducted by NCG and external specialists. We will also examine how we manage our contractors and implement any necessary improvements." — "4. Future Actions"View official source →
Phishing email and spoof emails after the Big Echo data breach
If the data did leak, the realistic risk for Big Echo customers is a convincing fake message. Phishing means posing as a real company to get someone to hand over a password or card number on a fake site. A sender who has your name, birthday, email and phone number can write something that looks very official.
Follow-up scams arrive as unexpected emails, text messages and calls, so links or attachments you do not recognize are best left unopened. Even a message offering an apology or a coupon is safer to ignore. Go to the official Big Echo or Daiichikosho site yourself instead of tapping a link.
Daiichikosho never asks for a password: hotline and email desk
Daiichikosho says it will never ask customers for a password or credit card details. Any message that does is not from the company.
The toll-free number 0120-732-079 opened on October 9 and is staffed from 10 a.m. to 5 p.m. Japan time, Monday to Friday except public holidays. Numbers starting 0120 are free only from phones in Japan. Customers abroad, or anyone who cannot get through by phone, can use the email desk at incident-desk@dkkaraoke.co.jp.
"Please also note that we will never ask you for your password, credit card information, or other such details. We kindly ask you to remain vigilant." — "3. Request to Our Customers"View official source →
FAQ
- I only booked a room at Big Echo once. Could my data be included?
- It could. Daiichikosho says the records come from customers who registered for membership or made reservations at its stores, so a one-time booking falls inside that group. The company has not offered a way to check individual records as of October 9.
- Can someone use my Big Echo points with the leaked data?
- Not with that data alone, according to Daiichikosho. Passwords were not part of the records, and the company says it has seen no unauthorized use of points so far.
- How do I contact Daiichikosho about the breach?
- Daiichikosho opened a toll-free line, 0120-732-079, on October 9. It answers from 10 a.m. to 5 p.m. Japan time on weekdays. If you cannot get through by phone or would rather write, email incident-desk@dkkaraoke.co.jp.
Related articles
 Japan foreign ministry leak may hit 3,600 recordsJapan's foreign ministry says names and email addresses in about 3,600 records may have leaked, including 900 outsiders. No classified or passport data.
 Japan's data leaks hit 260 million since AprilJapan's privacy regulator says unauthorized access affected data on a cumulative 260 million people from April to mid-October, with 830 reports in October.
 GMO's Onamae.com Desktop Cloud hacked, data leakedAttackers broke into Onamae.com Desktop Cloud, GMO Internet's VPS for FX trading, stole trading logins and leaked data after GMO refused a ransom.
 Japan data breach list: cases by date and causeThis Japan data breach list sorts disclosed cases newest first. Skyticket (14.64M records) and KDDI (12.23M users) lead. See what leaked, why, and what to do.