Member system hacked, up to 6.43M Bookoff records at risk
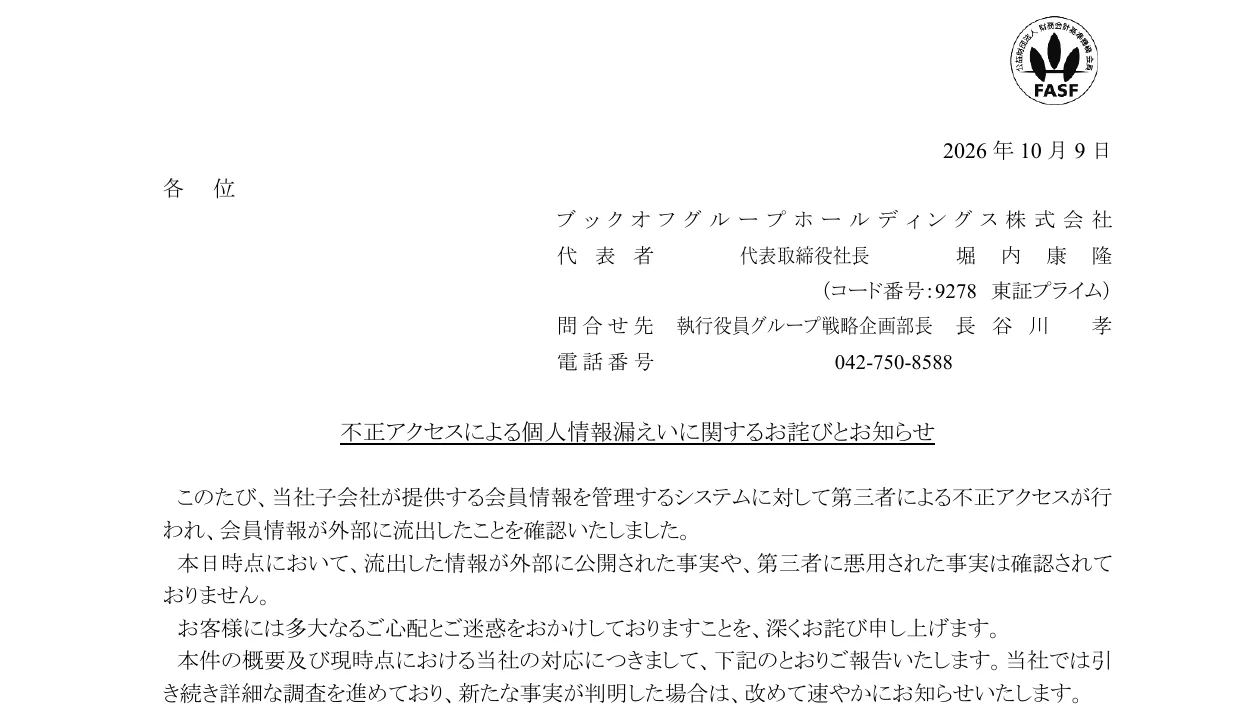
A third party got into the member management system run by a Bookoff subsidiary and pulled member data out of it. The subsidiary spotted the intrusion on October 6. A follow-up investigation confirmed that the data had been copied out of the system.
Bookoff Group Holdings announced the breach on October 9 in a timely disclosure, the stock exchange filing that listed Japanese companies must publish, and posted the same notice on the BOOKOFF website. The notice does not name the subsidiary or say which BOOKOFF service the system supports.
The Bookoff breach at a glance (from Bookoff Group Holdings' disclosure)
| Item | Detail |
|---|---|
| Unauthorized access confirmed | October 6, 2026 |
| Announced | October 9, 2026 |
| System | A subsidiary's member management system |
| Records that may have leaked | Up to about 6.43 million (counted by member number) |
The same week, Japanese travel site Skyticket also disclosed a breach. We covered it in Skyticket data breach: 3 incidents, up to 14.64M.
6.43M counts member numbers, not people
The 6.43 million figure is a count of member numbers that may have leaked, and Bookoff says it is not the number of people affected. The real headcount was not known at the time of the announcement. (Update: in its second report on October 13, 2026, Bookoff said 6,383,279 people are affected: 6,170,908 active and 212,371 former members, with records sharing an email address counted as one person. In its third report on November 6, it said the cause was an access-control flaw in part of the system that handles member data. Sources: Bookoff Group Holdings' timely disclosure, ScanNetSecurity.)
At that point Bookoff was still working out how many people were involved and exactly which of their data may have leaked, and said it would publish an update once it knew more.
"2026 年 10 月 6 日(火)、当社子会社の会員管理システムへの第三者による不正アクセスを確認いたしました。" / "最大 約 643 万件" / "漏洩した可能性のある会員番号の件数であり、対象となる方の実際の人数ではありません。" — sections 1 and 2View official source →
Names, addresses and password hashes, but no card data
Nine fields may have leaked, from names and addresses to password hashes, but no credit card data. Here is the full list.
Member data that may have leaked (from Bookoff Group Holdings' disclosure)
| Group | Fields |
|---|---|
| Personal details | Name, date of birth, gender |
| Contact details | Email address, phone number, postal code and address |
| Account details | Password hash, point card number, member number |
Credit card and other payment data were never stored in the hacked system, so they are not part of the leak. Bookoff has not found any member data that was changed. As of October 9, it also had no evidence that the stolen data had been posted online or misused.
Password hashes cannot be read as is, Bookoff says
The leaked passwords are hashes, so they cannot be read as is. A password hash is the result of running a password through a fixed calculation that turns it into a different string. Bookoff calls it an encrypted password.
"氏名、生年月日、性別、メールアドレス、電話番号、郵便番号・住所、パスワードのハッシュ値" / "暗号化されたパスワードであり、そのままでは読み取りできない情報です。" — section 2View official source →
Bookoff blocked the attacker, reports to privacy regulator
After confirming the break-in, Bookoff cut off traffic from the attacker and blocked outside access to the system. It also fixed a vulnerability in the system. Bookoff says the route it has identified is now closed and it is still monitoring.
The company is running an emergency check across all of its systems. It is also adding security measures on both the network and application side.
Bookoff is reporting the breach to the Personal Information Protection Commission, Japan's privacy regulator, among other steps. As the investigation identifies affected members, Bookoff will contact each of them individually.
"当社は、不正アクセスの確認後、攻撃元からの通信を遮断し、脆弱性を是正し、対象システムへの外部からのアクセスを遮断する措置を講じました。" — section 4View official source →
Watch for fake emails, texts and calls posing as Bookoff
If the stolen data is misused, members could get emails, texts or calls pretending to be from Bookoff or its partners. Bookoff asks members to do three things.
- Be wary of suspicious emails, texts and calls that claim to come from the Bookoff group
- Do not open links or attachments in messages you did not expect
- Do not enter personal details or login information in response to those messages
Bookoff says no group company will ever ask for any of the following by email, text or phone. A message that asks for them is not from Bookoff, whatever name it uses.
- Passwords or verification codes
- Credit card details
- Bank account details
Contact Bookoff by web form or at 0570-01-2902
Bookoff Group Holdings takes questions about the breach through a dedicated web form and a phone line. The number is 0570-01-2902, a Navi Dial line (a Japanese shared-cost number), open 10:00 to 18:30 Japan time. The form is on the dedicated contact page.
Members who receive a suspicious message or notice activity on their account they do not recognize can use these channels. The investigation is ongoing, and the company says it will share new findings as they come in.
"当社グループから、メール、SMS、電話等により、パスワード、認証コード、クレジットカード情報、銀行口座情報等をお尋ねすることはありません。" — section 3View official source →
FAQ
- Does 6.43 million mean 6.43 million people were affected?
- No. The figure counts member numbers that may have leaked, not people. Bookoff was still working out how many people were affected; its October 13 second report put the figure at 6,383,279 people (6,427,735 member records).
- Was credit card data leaked in the Bookoff breach?
- No. Bookoff says the hacked member system never held credit card or other payment data, so none of it is part of the leak.
- How do I contact Bookoff about the breach?
- Bookoff set up a dedicated web form and a phone line, 0570-01-2902, open 10:00 to 18:30 Japan time.
Related articles
 Japan foreign ministry leak may hit 3,600 recordsJapan's foreign ministry says names and email addresses in about 3,600 records may have leaked, including 900 outsiders. No classified or passport data.
 Japan's data leaks hit 260 million since AprilJapan's privacy regulator says unauthorized access affected data on a cumulative 260 million people from April to mid-October, with 830 reports in October.
 GMO's Onamae.com Desktop Cloud hacked, data leakedAttackers broke into Onamae.com Desktop Cloud, GMO Internet's VPS for FX trading, stole trading logins and leaked data after GMO refused a ransom.
 Japan data breach list: cases by date and causeThis Japan data breach list sorts disclosed cases newest first. Skyticket (14.64M records) and KDDI (12.23M users) lead. See what leaked, why, and what to do.