JAL and JTA reservation data exposed in an Amadeus breach
An intruder got into a system run by Amadeus, JAL's technology vendor, and part of JAL and JTA's reservation records was exposed. JAL calls it data that "had been accessed externally." The traces start on August 10, 2023 and end on September 23, 2026.
The breach at a glance (from JAL's notice)
| What | When or who |
|---|---|
| Amadeus reported to JAL | October 23, 2026 |
| JAL and JTA went public | October 28, 2026 |
| Vendor | Amadeus IT Group, S.A. |
| Traces of outside access | August 10, 2023 – September 23, 2026 |
| People affected | About 92,000 in total |
Japan has seen a run of breach disclosures this autumn. Earlier cases are listed in Japan data breach list: cases by date and cause.
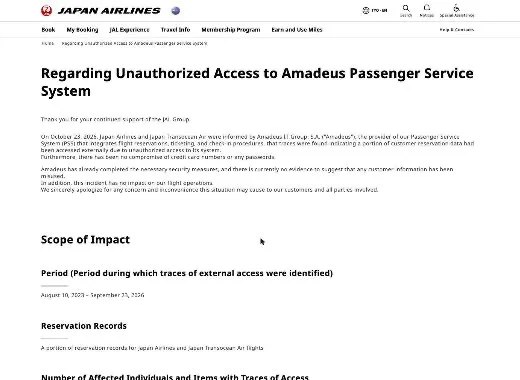
Amadeus told JAL on October 23; JAL went public on the 28th
Amadeus reported the break-in to JAL on October 23, and JAL and JTA announced it five days later in a joint notice. By then, according to JAL, Amadeus had already finished the security work it needed to do. JAL has not said how the intruder got in.
"traces were found indicating a portion of customer reservation data had been accessed externally due to unauthorized access to its system." / "Amadeus has already completed the necessary security measures" — opening paragraphsView official source →
Amadeus runs the airlines' passenger service system
Amadeus IT Group, S.A. is a Spanish company that supplies airlines with a passenger service system, the software an airline uses to handle reservations, ticketing and check-in. JAL and JTA run their bookings on it, and so does ANA.
The data was taken from Amadeus's system, not from a system inside JAL. That is why one vendor's problem now shows up at several airlines.
"the provider of our Passenger Service System (PSS) that integrates flight reservations, ticketing, and check-in procedures" — opening paragraphView official source →
"当社が旅客サービスシステムの提供を受けておりますAmadeus IT Group S.A.(本社:スペイン、以下「Amadeus社」)" — bodyView official source →
About 92,000 people affected, 2,000 with passport numbers
About 92,000 JAL and JTA customers are affected, and for about 2,000 of them the exposed data includes passport numbers and contact details. For the other 90,000 or so, five pieces of booking data were exposed: the PNR (the booking reference on an itinerary), name, flight date, route and class.
What was exposed, by group (from JAL's notice)
| People | Data exposed |
|---|---|
| About 90,000 | PNR, name, flight date, flight sector, class of service |
| About 2,000 | The five above, plus email address, phone number, passport number, nationality, frequent flyer number and ticket details (airline, flight number, ticket number, seat number) |
The exposed data for the larger group did not include email addresses or phone numbers. Only the smaller group of about 2,000 had contact details and passport numbers exposed together.
"Approx. 90,000 customers: Reservation code (PNR) / Name / Flight date / Flight sector / Class of service" / "Approx. 2,000 customers: In addition to the above, Email address / Phone number / Passport number / Nationality / Frequent flyer number / Airline name / Flight number / Ticket number / Seat number, etc." — Scope of ImpactView official source →
Credit card numbers and passwords were not exposed
In this break-in, no credit card numbers and no passwords were compromised. JAL also says it has no evidence so far that any of the exposed data has been misused. Flights are running as normal.
"Furthermore, there has been no compromise of credit card numbers or any passwords." / "there is currently no evidence to suggest that any customer information has been misused." / "In addition, this incident has no impact on our flight operations." — opening paragraphsView official source →
JAL contacts affected customers and opens an inquiry desk
JAL says it will get in touch with each affected customer. It also opened a phone desk for this case on October 29.
JAL's inquiry desk for this case (from JAL's notice)
| Item | Details |
|---|---|
| From overseas | +81-3-4332-7280 |
| From within Japan | 0120-25-6050 / 03-4332-7280 |
| Open from | Thursday, October 29, 2026 |
| Hours | 10:00 – 17:00 JST, weekdays, closed on Japanese national holidays |
To find out whether your booking was affected, wait for JAL's message or call the desk. Travelers outside Japan should keep the time difference in mind, since the desk only answers during Japanese business hours.
"In addition, we have established a dedicated inquiry desk regarding this matter." / "Operating Hours: 10:00 – 17:00 (JST), Monday through Friday (Excluding weekends and Japanese national holidays)" — Future Actions, Dedicated Inquiry DeskView official source →
Watch for emails and calls pretending to be JAL
JAL is warning customers about phishing emails, fake phone calls and websites that pose as the JAL Group. A message that quotes your booking code or flight date can still be fake, because those are exactly the details that were exposed.
Do not follow links in such messages. Go to JAL's own website, or call the inquiry desk number given above.
"including reminders to remain vigilant against phishing emails, fraudulent phone calls, and suspicious websites impersonating the JAL Group." — Future ActionsView official source →
ANA and Asiana also received reports from Amadeus
All Nippon Airways (ANA) said on October 29 that Amadeus had reported unauthorized access to ANA flight reservation data. In ANA's words, there are traces that some customers' personal data was viewed. As of that notice, ANA was still working with Amadeus to pin down the scope.
ANA has not said how many people are affected or which data was involved. It plans to tell affected customers once the details are confirmed.
Update: On October 30, ANA announced that traces show reservation data of about 37,800 people was viewed. About 1,700 of them also had data such as passport numbers involved, and credit card information and passwords were not included (per ANA's announcement and press reports such as Travel Voice).
"当社便の予約情報に第三者からの不正アクセスが発生し、当社のお客様の一部個人情報が参照された形跡があるとの報告を受けております。" / "現在、当社はAmadeus社と緊密に連携して影響範囲の特定を急いでいます。" — bodyView official source →
Asiana says Amadeus account login credentials were misused
South Korea's Asiana Airlines says the intruder used login credentials that had been issued to an account on Amadeus's system. Amadeus formally notified Asiana at 10:49 p.m. on October 20, 2026.
Asiana found signs that some customers' reservation numbers leaked, and it estimates the access took place between August 2023 and September 2026. That is close to the period JAL gives.
Asiana says it found no sign that its own system or database was breached. Amadeus told Asiana it has blocked the access and is watching the dark web, where stolen data is often traded.
"Amadeus의 시스템 계정에 부여된 로그인 인증정보를 이용한 비인가 접근으로 인해 발생하였습니다." / "당사 자체 시스템(DB)에 대한 침해 정황은 없음을 확인하였습니다." — bodyView official source →
What workplaces should review after a vendor breach
This break-in happened at Amadeus, the vendor that JAL and ANA rely on, not inside the airlines themselves. A single vendor breach has now led airlines in Japan and South Korea to warn their customers one after another.
Companies should check the systems their vendors run
Any company that keeps customer data in a vendor's system should review that vendor's security the same way it reviews its own. IPA, Japan's Information-technology Promotion Agency, ranks attacks on the supply chain and contractors second on its 2026 list of top security threats to organizations.
Keep a list of which vendor holds which customer data. When a vendor reports a breach, that list tells you right away which customers might be affected.
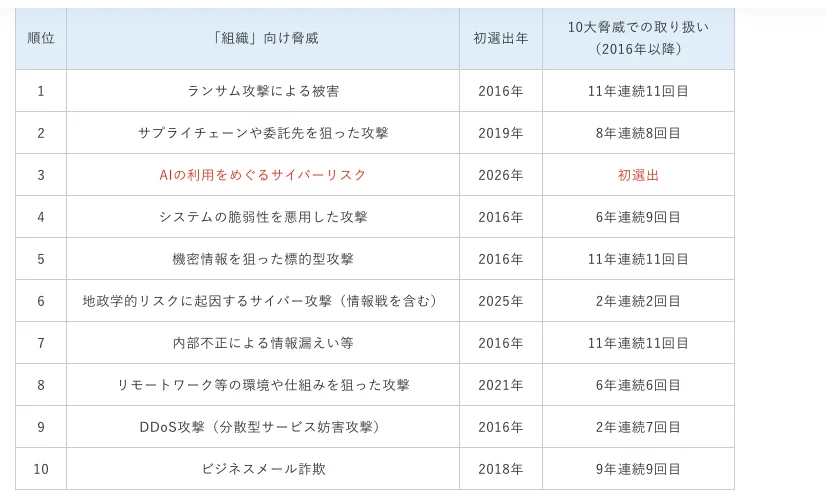
"サプライチェーンや委託先を狙った攻撃" — organization ranking tableView official source →
Staff should not open links in unexpected emails or texts
Everyone at work should avoid opening links in emails or text messages they were not expecting. Phishing means messages that pretend to come from a real company to lure people to a fake site, and a breach like this hands scammers real booking details to quote.
Japan's National Police Agency (NPA) advises bookmarking official sites or using official apps so you always reach the genuine page. Open the site from your bookmark or the app, not from a link in a message.
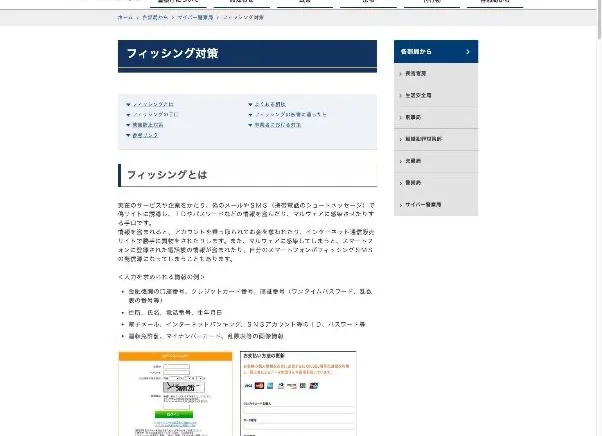
"あらかじめ公式サイトを「お気に入り」や「ブックマーク」に登録しておいたり、公式アプリを活用するなどして正しいサイトに接続するようにしてください。" — phishing countermeasuresView official source →
FAQ
- Were credit card numbers exposed in the JAL Amadeus breach?
- No. JAL says no credit card numbers or passwords were compromised.
- How do I know if my JAL booking was affected?
- Wait for JAL to get in touch or call its inquiry desk. JAL says it will contact affected customers one by one.
- What is the phone number for JAL's inquiry desk?
- From overseas, call +81-3-4332-7280. From within Japan, call 0120-25-6050 or 03-4332-7280. The desk is open 10:00 to 17:00 Japan time on weekdays, except Japanese national holidays.
Related articles
 Japan foreign ministry leak may hit 3,600 recordsJapan's foreign ministry says names and email addresses in about 3,600 records may have leaked, including 900 outsiders. No classified or passport data.
 Japan's data leaks hit 260 million since AprilJapan's privacy regulator says unauthorized access affected data on a cumulative 260 million people from April to mid-October, with 830 reports in October.
 GMO's Onamae.com Desktop Cloud hacked, data leakedAttackers broke into Onamae.com Desktop Cloud, GMO Internet's VPS for FX trading, stole trading logins and leaked data after GMO refused a ransom.
 Japan data breach list: cases by date and causeThis Japan data breach list sorts disclosed cases newest first. Skyticket (14.64M records) and KDDI (12.23M users) lead. See what leaked, why, and what to do.