So-net discloses a breach of 2.58 million customer records
Sony Network Communications has disclosed that an outside attacker got into So-net's member database, exposing 2,585,481 customer records from So-net and plala (S Course). So-net is a Japanese internet provider, and Sony Network Communications is the Sony Group company that runs it.
NTT Docomo sells plala (S Course) as a provider plan with Docomo Hikari, its fiber line. Docomo contracts the plan's operation out to Sony Network Communications. Sony Network Communications announced the breach on October 27 and updated its notice on October 29.
The total is a count of records rather than people, so the same person may be counted more than once. The table below splits it by service and by current or former membership.
Leaked member records by service (from So-net's notice)
| Service | Current members | Left in March 2026 or later | Total |
|---|---|---|---|
| So-net | 1,869,771 | 272,215 | 2,141,986 |
| plala (S Course) | 422,365 | 21,130 | 443,495 |
Each affected customer will get an individual apology from the company. For other breaches Japanese companies have disclosed, see Japan data breach list: cases by date and cause.
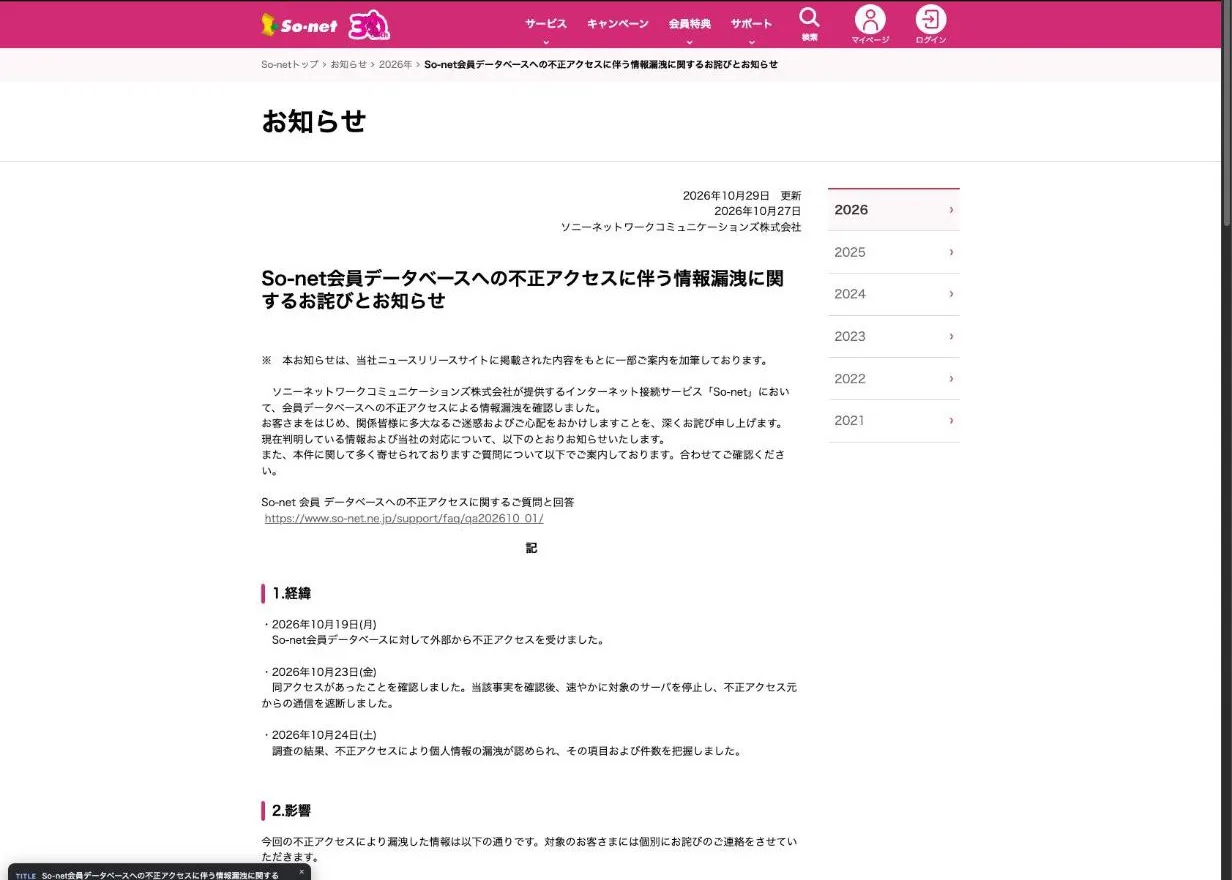
Attackers got in on October 19, found on October 23
The attacker accessed the database on October 19, 2026, and Sony Network Communications discovered the access four days later, on October 23. It then shut down the affected server and blocked traffic from the source of the attack.
The next day, October 24, the investigation confirmed that personal data had leaked and identified which fields and how many records were involved. The company went public three days after that, on October 27.
"So-net会員データベースに対して外部から不正アクセスを受けました。" / "同アクセスがあったことを確認しました。当該事実を確認後、速やかに対象のサーバを停止し、不正アクセス元からの通信を遮断しました。" — from section 1, BackgroundView official source →
Current members and those who left in March or later
Both current members and people who canceled in March 2026 or later are affected. The company still held former members' data because it keeps records for a period after cancellation to bill the last month of service and handle inquiries.
Anyone who canceled by the end of February 2026 is not affected. Sony Network Communications also says it has found no leak from NURO or its other services.
"※2026年2月末日までに退会された方の漏洩はございません。" — from section 2, ImpactView official source →
Names, birth dates and five other data fields were exposed
The same seven fields were exposed for So-net and plala (S Course) members: name, phone number, email address, user ID, date of birth, gender and internet connection ID. The user ID is the one you enter to sign in to My Page, So-net's account site. The connection ID is a separate credential that your router or PC uses to get online.
A handful of So-net records contained more sensitive data. In 16 cases, bank details were exposed: the bank and branch, plus the account type, number and holder's name.
Another seven records were notice letters So-net issues to members who need to reset a password. None of the bank or notice-letter records belonged to plala (S Course) customers.
54,401 email addresses also had their passwords exposed
For users of four So-net mail services, both the email address and the mailbox password were exposed. With that pair, someone else could sign in to the mailbox through a mail app or So-net Webmail.
Email addresses whose password leaked (from So-net's notice)
| Mail service | Free or paid | Addresses |
|---|---|---|
| Mail Service (G) | Free | 24,655 |
| A-Box additional mailbox | Paid | 17,672 |
| So-net VAIO Mail | Paid | 7,005 |
| PostPet Mail Account Service | Paid | 5,069 |
| Total | 54,401 |
The four services do not include the free basic mailbox that every So-net account gets on the so-net.ne.jp domain. So-net says it has found no sign that those passwords leaked.
"以下のメールサービスのメールアドレスおよびメールアドレスパスワードについて漏洩を確認しました。" — from section 2, ImpactView official source →
Login passwords and credit card data were not exposed
Apart from the seven notice-letter cases, the password for signing in to My Page was not exposed. Credit card data was not affected, since Sony Network Communications says it does not store card numbers. It does not hold bank PINs either.
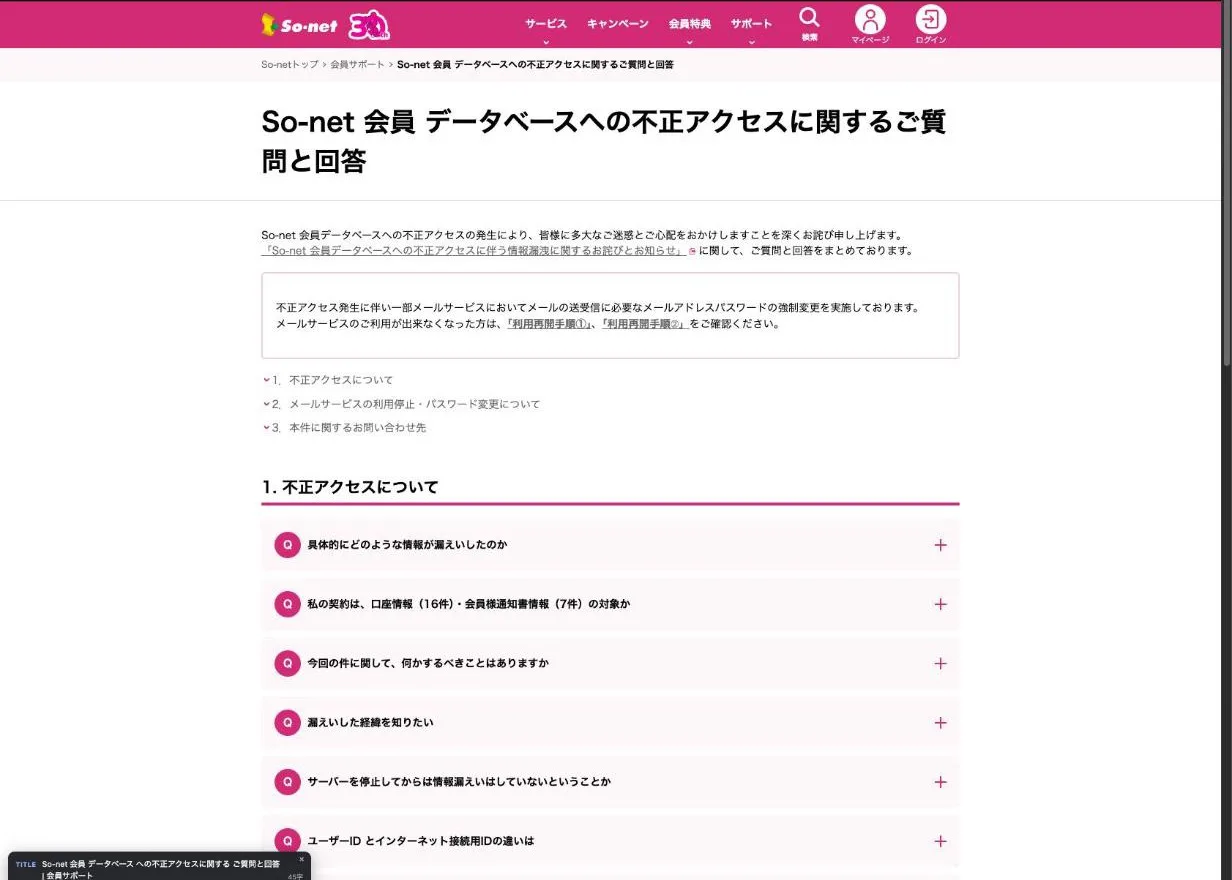
"マイページなどのログインに必要な「ユーザーIDパスワード」(会員様通知書情報の 7 件を除く)" / "当社ではクレジットカード情報を保持していないため、クレジットカードの漏えいはございません。" — from section 1, About the unauthorized accessView official source →
Sony reset email passwords, but the cause is unknown
Sony Network Communications began force-resetting the passwords of all 54,401 affected email addresses at around 10 a.m. on October 27. Left in place, the leaked passwords would have let a third party read those inboxes and send mail from those addresses.
The company has reported the breach to Japan's Personal Information Protection Commission. It has not said how the attacker got in, and it has named no flaw, malware or suspect. Its investigation into the cause and full scope is still underway.
What Sony Network Communications has done so far
| Step | When |
|---|---|
| Took the server offline and blocked the attacker's traffic | October 23 |
| Reset the passwords of the 54,401 email addresses | October 27, from about 10 a.m. |
| Reported to the Personal Information Protection Commission | By October 27 |
No new leak has been found since the server went offline. Once the cause is clear, the company plans to review its security measures and the way it manages customer data.
"被害拡大防止のため、項目2—②に該当するメールアドレスパスワードについては、2026年10月27日に当社にて初期化をおこないました。" / "また、本件については、個人情報保護委員会にも報告し、本事案の原因および影響範囲の詳細に関する調査を進めております。" — from section 4, Current statusView official source →
Docomo's plala (S Course) data leaked through a contractor
NTT Docomo was notified by Sony Network Communications on October 26 and posted its own notice for plala (S Course) customers the next day. Docomo gives the same count, 443,495 records, covering current users and customers who canceled within the past six months.
Docomo says customers on other plans, including plala on Docomo Hikari outside the S Course, are not affected. In Docomo's case, the data leaked from a contractor's database, not from its own systems.
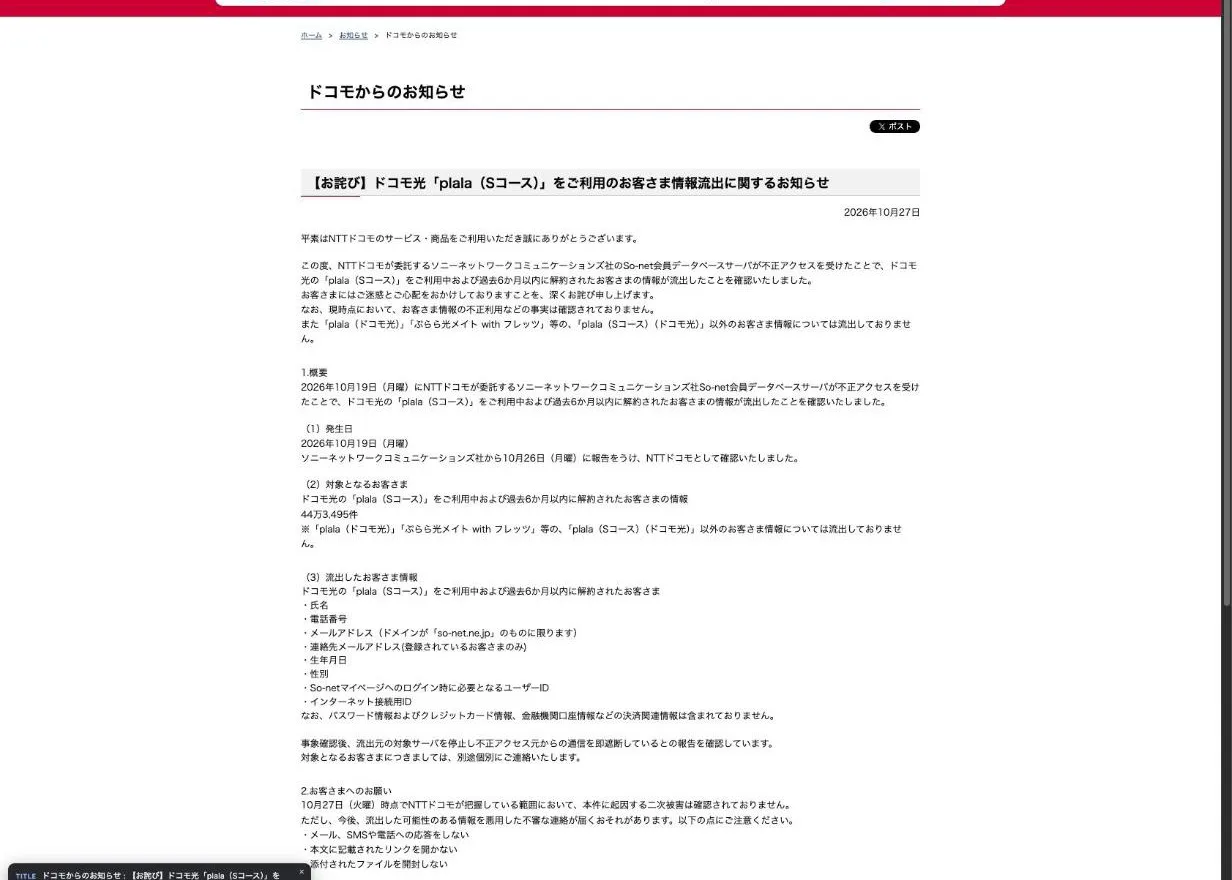
"ソニーネットワークコミュニケーションズ社から10月26日(月曜)に報告をうけ、NTTドコモとして確認いたしました。" / "「plala(ドコモ光)」「ぷらら光メイト with フレッツ」等の、「plala(Sコース)(ドコモ光)」以外のお客さま情報については流出しておりません。" — from section 1, SummaryView official source →
Watch for emails, texts and calls claiming to be So-net
Current and former So-net and plala (S Course) members should be wary of any unexpected email, text or call about this breach. With leaked names, phone numbers and email addresses, scammers can make a fake message look like it came from So-net. So-net asks members not to reply to such messages or open their links or attachments.
As of October 29, So-net says it has found no secondary harm from the breach. To check anything about your account, open So-net's site from a bookmark or by typing the address, not from a link in a message.
"10 月 29 日時点で当社が把握している範囲において、本件に起因する二次被害は確認されておりません。" / "本文に記載されたリンクを開かない" — from section 1, About the unauthorized accessView official source →
Users of the four mail services must reset passwords
Users of Mail Service (G), A-Box, So-net VAIO Mail and PostPet Mail can no longer use their old password. Set a new one on My Page, where you sign in with your user ID and login password. If you read mail in an app such as Outlook, update the saved password there too.
A new password can take anywhere from a few minutes to about 30 minutes to start working. If you used the old password on other sites, change it there too. A long, random password for each site keeps one leak from unlocking your other accounts.
"下記のメールサービスのメールアドレスおよび、メールアドレスパスワードが本件漏えいの対象であることから従来のパスワードでの利用を停止しております。" / "お手続きにはユーザーID・パスワードが必要となります。" — from section 2, Suspension and password change for mail servicesView official source →
Questions go to So-net's hotline at 0120-36-8887
So-net's dedicated hotline, 0120-36-8887, takes calls on weekdays and Saturdays from 10:00 to 18:00. It is also open on Sunday, November 1, and on the November 3 holiday. Docomo Hikari customers on plala (S Course) should call Docomo at 0120-035-700, which is open from 10:00 to 19:00 every day.
Both numbers are toll-free within Japan. So-net is contacting the members behind the 16 bank-detail records and the seven notice-letter cases individually, through My Page or by email.
"So-net特設ダイヤル:0120-36-8887(平日・土曜:10時00分~18時00分)" / "※11月1日(日)、11月3日(祝)もお電話を承ります。" — from section 7, Customer contactView official source →
"(受付時間 10時00分~19時00分(土日祝含む))" — from section 3, ContactView official source →
What companies and employees should take from this breach
This breach points to two habits that limit the damage. Companies need to know which outside firms hold their customers' data, and employees should not trust a message just because it refers to a real leak.
Check how your vendors protect customer data
Docomo's customer data leaked from a database that another company ran on its behalf. Japan's Information-technology Promotion Agency (IPA) puts attacks on supply chains and contractors second on its 2026 list of the top ten threats to organizations. A company that keeps a list of which contractors hold which customer data can tell, on the day a contractor reports a breach, which of its customers are affected.
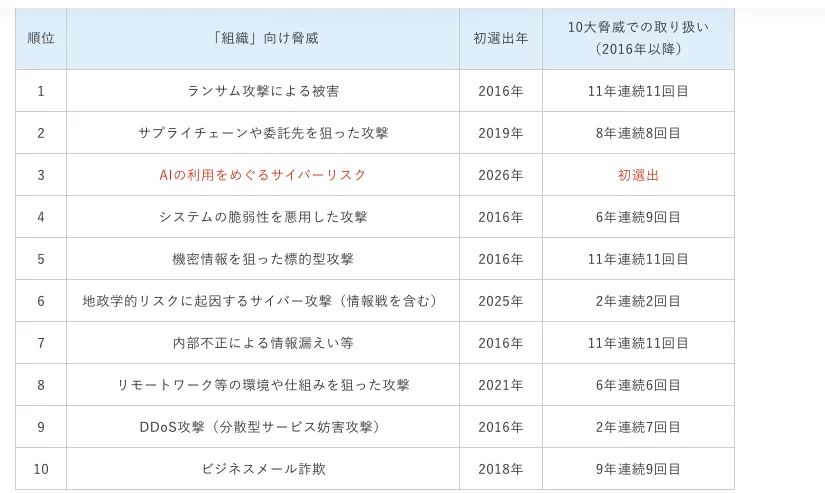
"サプライチェーンや委託先を狙った攻撃" — from the 2026 organizations listView official source →
Don't click links in breach-themed emails
Phishing emails often use phrases like "data leak" or "unauthorized access detected" to push you into signing in. In phishing, a message poses as a real company to lure you to a fake site where you type in your details. Japan's National Police Agency says this kind of urgent wording shows up in many fake emails, and it advises reaching sites from a saved bookmark or the official app.
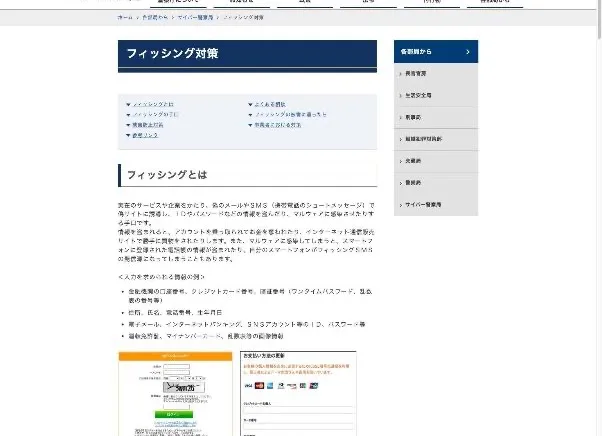
"電子メール等の文面は、「個人情報の漏えい」、「不正アクセス検知」、「取引の停止」等、切迫感を煽り、ログインさせようとするものが多数確認されています。" / "あらかじめ公式サイトを「お気に入り」や「ブックマーク」に登録しておいたり、公式アプリを活用するなどして正しいサイトに接続するようにしてください。" — from the phishing methods and countermeasures sectionsView official source →
FAQ
- Were credit card numbers exposed in the So-net breach?
- No. Sony Network Communications says it does not hold credit card data at all, so none could leak.
- Was my So-net My Page login password leaked?
- No, with one small exception. Seven password-reset notice letters were exposed, and those seven people are being contacted individually. Everyone else's login password was not part of the leak.
- I use one of the affected So-net mail services. What should I do?
- Set a new email password on So-net's My Page. Until you do, that address can't send or receive mail. If you read mail in an app such as Outlook, enter the new password there too.
Related articles
 Japan foreign ministry leak may hit 3,600 recordsJapan's foreign ministry says names and email addresses in about 3,600 records may have leaked, including 900 outsiders. No classified or passport data.
 Japan's data leaks hit 260 million since AprilJapan's privacy regulator says unauthorized access affected data on a cumulative 260 million people from April to mid-October, with 830 reports in October.
 GMO's Onamae.com Desktop Cloud hacked, data leakedAttackers broke into Onamae.com Desktop Cloud, GMO Internet's VPS for FX trading, stole trading logins and leaked data after GMO refused a ransom.
 Japan data breach list: cases by date and causeThis Japan data breach list sorts disclosed cases newest first. Skyticket (14.64M records) and KDDI (12.23M users) lead. See what leaked, why, and what to do.